GeoServer Security Update - September 2026
This post provides a recap of the security advisories published over the summer of 2026, covering recently published Common Vulnerability and Exploits (CVE), along with a supply chain advisory affecting the GeoServer project. This activity has resulted in an update to our security policy covering AI-assisted vulnerability reports.
If you are responsible for a GeoServer instance, the short version is: please update to GeoServer 3.0.1, GeoServer 2.28.5, or GeoServer 2.27.6.
The GeoServer project follows a coordinated vulnerability disclosure policy: vulnerabilities are fixed for both stable and maintenance releases, prior to CVE details being published. The goal is to give everyone an opportunity to update prior to public disclosure.
August zero-day
In August GeoServer experienced a zero-day vulnerability (an exploit in the wild with no known fix). The problem had already been reported privately by several independent researchers, and a fix scheduled for the GeoServer 3.0.1 release.
The zero-day situation arose because a third party (unconnected to the project or to the researchers who had reported the issue) disclosed the vulnerability publicly on social media. The effect was immediately evident, with scans for this vulnerability detected within hours of the public social media post.
The speed of this response was remarkable and resulted in news coverage and an urgent call to update on our user forum. We would like to thank the reporter Ravie Lakshmanan who first notified project leadership via the Open Source Geospatial Foundation.
GeoServer 3.0.1, GeoServer 2.28.5, and GeoServer 2.27.6:
-
CVE-2026-76904 Unauthenticated PostGIS SQL injection in the
jsonArrayContainsfilter function (Critical)This releases addresses the GeoTools CVE-2026-76904 SQL Injection vulnerability that: requires a Text or JSON column; affects PostGIS 12 and up.
This experience reaffirms the importance of following the coordinated vulnerability disclosure policy, and asking everyone to update when new releases are made available.
Previously published CVEs
The following CVEs were published on June 11, 2026, alongside the GeoServer 3.0.0 release.
GeoServer 2.27.3, and 2.26.4:
-
CVE-2025-58175 Server-Side Request Forgery (SSRF) Vulnerability in XML entity resolution (Medium)
-
CVE-2025-52465 Arbitrary file write vulnerability in Master Password Dump Page (High)
GeoServer 2.27.0:
-
CVE-2024-45747 Server-Side Template Injection (SSTI) vulnerability in processing FreeMarker templates (High)
-
CVE-2025-27511 JNDI Vulnerability in DB2 Store Connection (High)
Supply chain advisory
Supply chain advisories have the possibility to affect the integrity of the software you download:
-
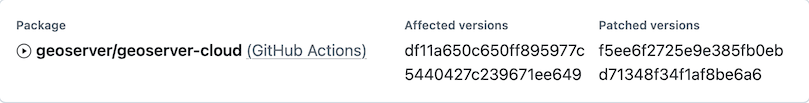
GHSA-cpc9-c4h3-2jwx GitHub Actions workflow in GeoServer Cloud (April 2026)
A security researcher Aviv Donenfeld reported an issue in a geoserver-cloud repo GitHub actions workflow.
While GeoServer uses GitHub for source code management and quality assurance workflows, such workflows are not used to build or publish download artifacts. A review was made to confirm all pull requests during the time of vulnerability were by trusted parties, secrets were rotated, and the workflow issue was addressed.
This was first time the project has worked with an infrastructure advisory like this. We have marked the advisory as “geoserver/geoserver-cloud (GitHub Actions)” as it does not correspond with a release of GeoServer, and as a result does not qualify for a CVE number.
It is important to note that no GeoServer releases were affected. GeoServer releases are made using a Jenkins build server publishing artifacts to both SourceForge and OSGeo infrastructure.
AI-assisted vulnerability reports
Like many other software projects, we are experiencing a wave of vulnerability reports generated with AI assistance.
We have both established a general AI Policy, and updated our Security Policy, to acknowledge the use of these tools and provide guidance:
- The human reporter is responsible for verifying the issue is real and reproducible before submitting.
- Reports must include a working reproduction (code, request, or config) against a supported GeoServer series, not just a plausible-sounding description.
- Reports that turn out to be hallucinated or unverifiable will be closed without further engagement.
Especially with AI reports, which are often very verbose, being on hand to clarify is greatly appreciated.
These reports can take quite some time to review, or even determine when such reports are duplicates. It also helps if you are in a position to test and verify fixes as they are addressed. Anything we can do to make the work of the geoserver-security team easier will be of assistance.
Q: How can I help?
If your organization depends on GeoServer, please consider sponsoring the project, or have your staff directly participate in geoserver-security work.
We are also looking to establish project membership for public institutions facing restrictions on sponsorship and participation.
Q: How often should I upgrade GeoServer?
GeoServer operates with a time-boxed release cycle, maintaining “stable” and “maintenance” releases, over the course of a year.
- GeoServer 3.0.x is the current stable release
- GeoServer 2.28.x is the current maintenance release
Please upgrade to a supported release at least once a year to continue receiving security fixes. See the Upgrading existing versions (User Guide) for guidance.
Q: How do I report a vulnerability?
Please see our security policy for instructions on reporting vulnerabilities privately using GitHub security advisories.
 Atom feed